What Is GDPR?
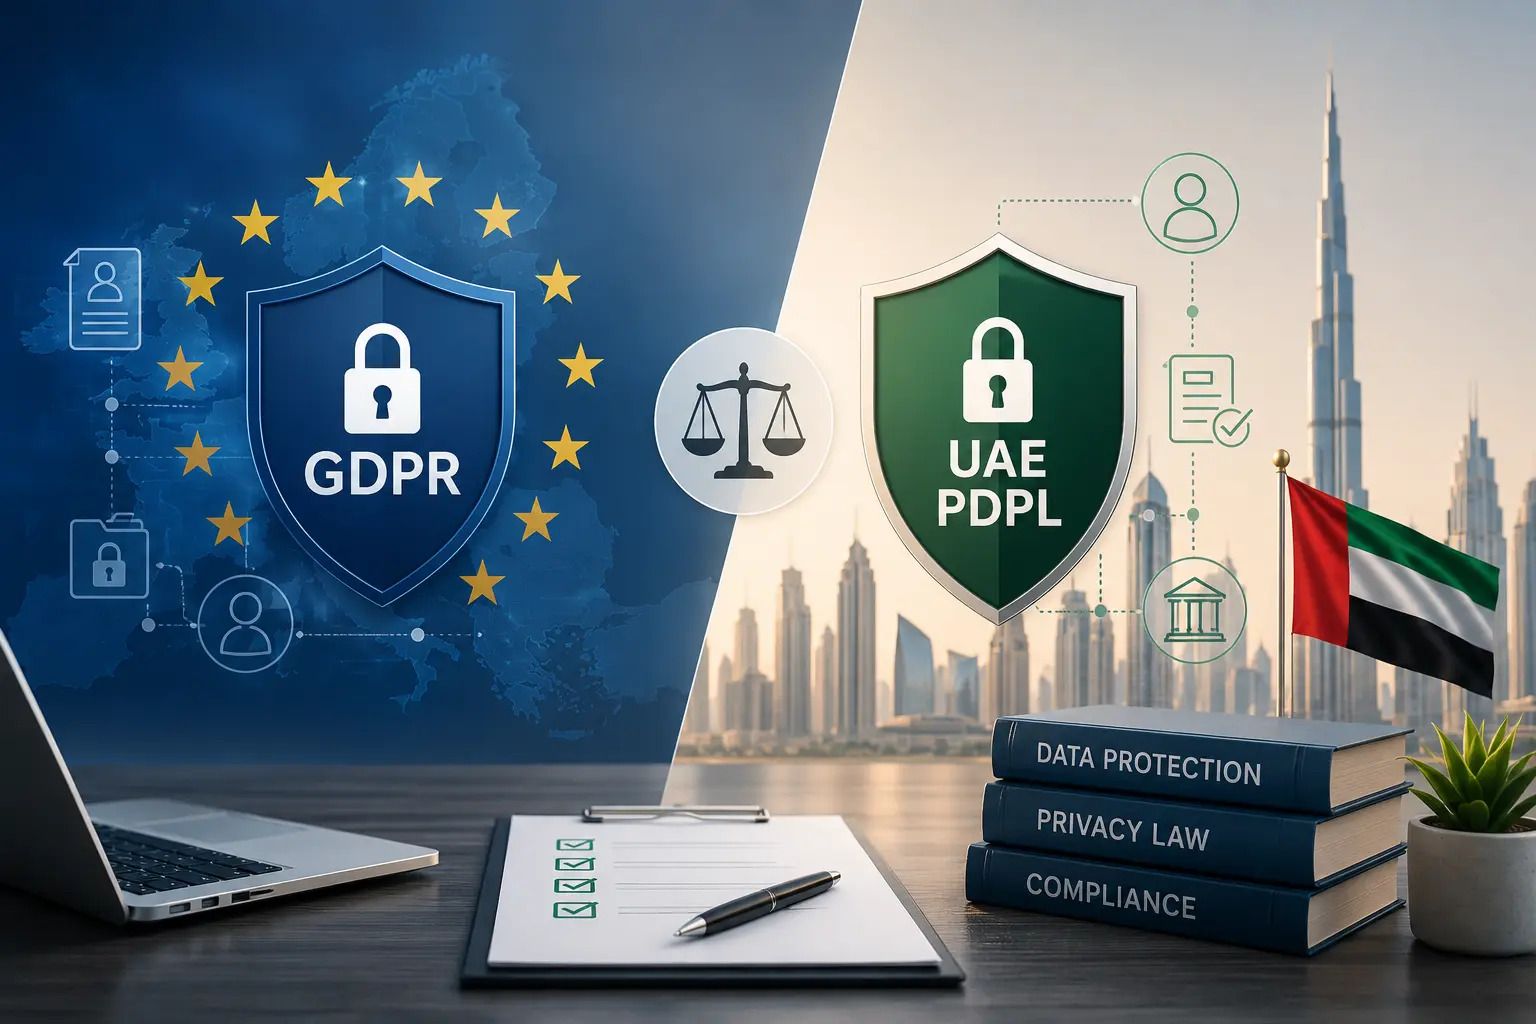
The General Data Protection Regulation (GDPR) is a comprehensive and stringent privacy and
security law drafted and passed by the European Union (EU). Implemented in 2018, it imposes
obligations onto organizations anywhere, so long as they target or collect data related to people in
the EU. The GDPR's primary goal is to give individuals profound control over their personal data and
to simplify the regulatory environment for international business by unifying the regulation within the
EU. It is widely considered the global gold standard for data privacy.
security law drafted and passed by the European Union (EU). Implemented in 2018, it imposes
obligations onto organizations anywhere, so long as they target or collect data related to people in
the EU. The GDPR's primary goal is to give individuals profound control over their personal data and
to simplify the regulatory environment for international business by unifying the regulation within the
EU. It is widely considered the global gold standard for data privacy.
What Is the UAE PDPL?
The UAE Personal Data Protection Law (PDPL), officially known as Federal Decree Law No. 45 of
2021, is the first comprehensive federal law in the United Arab Emirates dedicated to regulating the
processing of personal data. It aims to protect the privacy and rights of individuals regarding their
personal information while establishing a robust framework for data governance that aligns with
international best practices, thereby boosting confidence in the UAE's digital economy.
2021, is the first comprehensive federal law in the United Arab Emirates dedicated to regulating the
processing of personal data. It aims to protect the privacy and rights of individuals regarding their
personal information while establishing a robust framework for data governance that aligns with
international best practices, thereby boosting confidence in the UAE's digital economy.
GDPR vs UAE PDPL: Key Differences
While the UAE PDPL was heavily inspired by the GDPR and shares many of its core principles—such
as transparency, purpose limitation, and data minimization—there are crucial differences that
businesses operating in or with the UAE must understand. These differences primarily revolve around
the scope of application, specific consent requirements, and the nuances of data subjects' rights.
as transparency, purpose limitation, and data minimization—there are crucial differences that
businesses operating in or with the UAE must understand. These differences primarily revolve around
the scope of application, specific consent requirements, and the nuances of data subjects' rights.
Scope and Applicability
The GDPR has an extraterritorial scope; it applies to any company, regardless of its location, that
processes the personal data of EU residents, either by offering them goods/services or monitoring
their behavior. The UAE PDPL applies to any organization established in the UAE that processes
personal data, as well as organizations located outside the UAE that process the personal data of
individuals residing within the UAE.
processes the personal data of EU residents, either by offering them goods/services or monitoring
their behavior. The UAE PDPL applies to any organization established in the UAE that processes
personal data, as well as organizations located outside the UAE that process the personal data of
individuals residing within the UAE.
Consent and Legal Basis
Both frameworks heavily emphasize the need for a lawful basis to process data, with consent being a
primary mechanism. Under GDPR, consent must be freely given, specific, informed, and
unambiguous. The UAE PDPL also requires explicit consent; however, it provides specific exemptions
where consent is not required, such as when processing is necessary to protect the public interest,
for public health reasons, or to fulfill obligations under other UAE laws.
primary mechanism. Under GDPR, consent must be freely given, specific, informed, and
unambiguous. The UAE PDPL also requires explicit consent; however, it provides specific exemptions
where consent is not required, such as when processing is necessary to protect the public interest,
for public health reasons, or to fulfill obligations under other UAE laws.
Data Subject Rights
Both laws grant individuals significant rights over their data, including the right to access, correct,
erase (the "right to be forgotten"), and restrict the processing of their data. However, the
mechanisms for enforcing these rights and the specific timelines for organizations to respond to data
subject requests may vary between the two jurisdictions.
erase (the "right to be forgotten"), and restrict the processing of their data. However, the
mechanisms for enforcing these rights and the specific timelines for organizations to respond to data
subject requests may vary between the two jurisdictions.
Data Breach Notification
Data security is paramount in both regulations. The GDPR requires organizations to report significant
data breaches to the relevant supervisory authority within a strict 72 hour window. The UAE PDPL
also mandates the reporting of data breaches that pose a risk to the privacy, confidentiality, or
security of the data subject, requiring notification to the UAE Data Office and, in certain cases, to the
affected individuals, though the specific timeframes are detailed in the executive regulations.
data breaches to the relevant supervisory authority within a strict 72 hour window. The UAE PDPL
also mandates the reporting of data breaches that pose a risk to the privacy, confidentiality, or
security of the data subject, requiring notification to the UAE Data Office and, in certain cases, to the
affected individuals, though the specific timeframes are detailed in the executive regulations.
Cross Border Data Transfers
Transferring personal data outside the country's borders is strictly regulated to ensure the data
remains protected. The GDPR allows transfers to countries deemed to have an "adequate" level of
protection or through specific safeguards like Standard Contractual Clauses. Similarly, the UAE PDPL
sets strict conditions for cross border transfers, generally requiring that the destination country
provides an adequate level of protection as determined by the UAE Data Office, or that specific
contractual or bilateral agreements are in place.
remains protected. The GDPR allows transfers to countries deemed to have an "adequate" level of
protection or through specific safeguards like Standard Contractual Clauses. Similarly, the UAE PDPL
sets strict conditions for cross border transfers, generally requiring that the destination country
provides an adequate level of protection as determined by the UAE Data Office, or that specific
contractual or bilateral agreements are in place.
When Can GDPR Apply to UAE Businesses?
A common misconception is that UAE businesses are exempt from GDPR. A UAE based company
must comply with GDPR if it offers goods or services (even for free) to individuals in the EU, or if it
monitors the behavior of individuals within the EU (for example, through targeted online advertising or
tracking cookies on a website).
must comply with GDPR if it offers goods or services (even for free) to individuals in the EU, or if it
monitors the behavior of individuals within the EU (for example, through targeted online advertising or
tracking cookies on a website).
Data Protection Compliance Checklist for Businesses
- Has the organization appointed a qualified Data Protection Officer (DPO) if required by law?
- Are there clear, documented procedures for obtaining and managing explicit consent from customers?
- Does the company have a robust system in place to handle data subjects' requests within the legal timeframes?
- Are all data processing activities mapped and recorded in a Record of Processing Activities (RoPA)?
Why Employee Training Matters for Data Privacy Compliance
Even the most sophisticated technical security measures can be undermined by human error.
Employees are often the first line of defense and the weakest link in data privacy. Comprehensive
training is essential to ensure staff understand the legal requirements, recognize sensitive data, and
know how to handle it securely. NKO Training offers a course in International Compliance,
Governance and Ethics
Employees are often the first line of defense and the weakest link in data privacy. Comprehensive
training is essential to ensure staff understand the legal requirements, recognize sensitive data, and
know how to handle it securely. NKO Training offers a course in International Compliance,
Governance and Ethics
that covers essential data protection principles to enhance your team's awareness and compliance
capabilities.
capabilities.
FAQs About GDPR and UAE PDPL
What are the fines for non compliance? Both laws carry severe penalties. GDPR fines can reach up to
€20 million or 4% of global annual turnover. The UAE PDPL also outlines significant administrative
penalties for violations.
€20 million or 4% of global annual turnover. The UAE PDPL also outlines significant administrative
penalties for violations.
Do small businesses need to comply with these laws? Yes, data protection laws generally apply to all
businesses that process personal data, regardless of size, though the specific administrative burdens
may vary.
businesses that process personal data, regardless of size, though the specific administrative burdens
may vary.
Subscribe to our newsletter
Policy Pages
Sign up
Create your account
Sign in to your account to continue and access your dashboard.